Table of contents
Related resources


Best SAST Tools in 2026: Top 10 Solutions Ranked

A SAST tool that finds 3,000 issues on the first scan has not found 3,000 vulnerabilities. It has found a tuning project. The tools worth paying for in 2026 are the ones that tell you which handful of those are reachable, show the finding where the developer is working, and hand back a fix that compiles.
This guide ranks 10 SAST tools on that standard and answers the three questions buyers ask most: which languages are actually covered, how the tool fits into IDEs and source control, and how it is priced.
What are SAST tools?
SAST (Static Application Security Testing) tools analyze an application’s source code to identify potential security vulnerabilities without executing the code. They are crucial for finding security flaws early in the development lifecycle, helping developers address issues before they become more costly and difficult to fix. This guide covers the best SAST tools available in 2026 and how to evaluate them.
Unlike dynamic analysis techniques, SAST operates without executing the program, focusing entirely on the static codebase. This approach allows SAST tools to detect security flaws through code scanning, such as injection vulnerabilities, insecure coding practices, and critical misconfigurations before an application is ever run in production or tested by end-users. For a comparison of static and composition-based approaches, see our guide to SAST vs SCA.
SAST covers only the code your team writes, so most programs pair it with other application security testing tools. DAST tests the running application, API security testing checks the endpoints it exposes, and software composition analysis (SCA) checks the open source you pull in.
What modern SAST tools do
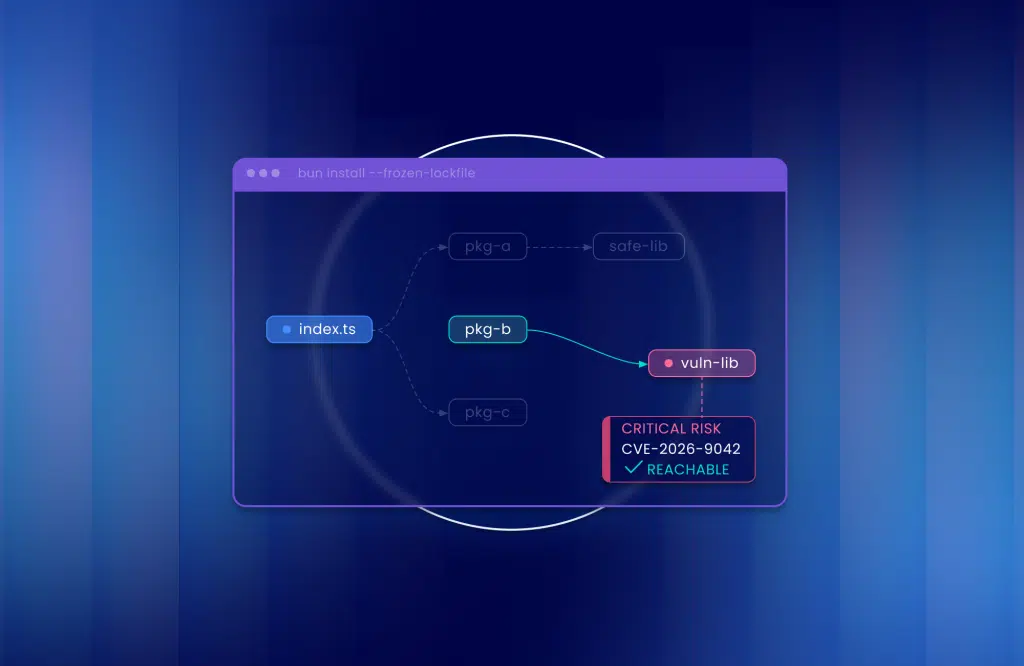
- Prioritize real risk: they demonstrate exploitability by tracing proof paths through the code, so developers see whether an issue is reachable and filter out the rest. Taint analysis, which follows untrusted input from where it enters the code to the sensitive operation it reaches, is how most tools trace those paths.
- Fit developer workflow: lightweight scans run inside IDEs and pull requests with low latency, so vulnerabilities are caught as code is written or reviewed.
- Control noise: they baseline results across scans, suppress duplicates, and surface only new or changed issues; AI clusters similar findings and cuts false positives.
- Automate remediation: AI powered fix suggestions and triage workflows shorten the gap between finding a vulnerability and shipping the fix.
- Keep up with technology: they cover new languages, frameworks, and the coding patterns AI assistants produce. AI-generated code is the clearest example, since it reaches the repository faster than manual review can check it.
Editor’s note: Updated information about SAST tools to reflect features and capabilities in 2026.
Which languages do SAST tools support?
Language coverage is the first filter, and it is less uniform than vendor pages suggest. Three things to check: whether your primary languages run on the vendor’s current engine (older engines usually mean more false positives), whether legacy languages you still maintain are covered at all, and whether the tool handles mixed-language repositories without separate configuration.
Mend SAST lists 28 languages across two engine generations. Its Gen 2 engines cover C/C++, C#, Go, Java, JavaScript and Node.js, Python, Ruby, Rust, Scala, Swift, and TypeScript, with custom taint sources, sinks, and sanitizers and toggleable low-probability findings. Gen 1 engines cover ABAP, Android Java, Apex, ASP Classic, COBOL, ColdFusion, Groovy, Kotlin, Objective-C, PHP, PL/SQL, R, VB.NET, Visual Basic, and Xamarin, which matters if you maintain a mainframe or Salesforce estate alongside modern services.
For the other nine tools, confirm the current list on each vendor’s documentation; coverage changes several times a year.
How SAST tools integrate with IDEs and source control
The integration question has two halves, and buyers usually only ask one.
Source control integration decides where findings appear: as a check on the pull request, as a comment on the changed lines, or as an issue. Most tools in this list support GitHub; coverage of GitLab, Bitbucket, and Azure DevOps varies, and so does whether the scan is differential (changed code only) or a full rescan on every PR. Differential scanning is what keeps PR checks under a few minutes on large repositories. Mend SAST scans changed code at commit and reports through the GitHub, GitLab, Bitbucket Cloud, and Azure DevOps integrations.
IDE integration has changed in the past year. The old model was a plugin that scans on save. The new model is a connection to the AI coding agent itself, so generated code is checked before the developer accepts it. Mend.io does this through its MCP server for Cursor, Windsurf, and VS Code Copilot: when the agent generates code or adds a dependency, it calls Mend.io to check the code for CWEs and the library for CVEs, and gets guidance back to fix what it finds.
When you evaluate, ask for a demo on your own repository with your own PR flow, and time the check.
How SAST tools are priced
SAST pricing follows one of four models, and the model matters more than the list price.
- Per developer or contributor: you pay for the people who commit code. Predictable for stable teams, expensive when contractors and AI agents inflate the contributor count.
- Per application or repository: you pay for what is scanned. Suits organizations with a defined application portfolio; penalizes microservice sprawl.
- Per scan or lines of code: usage-based. Cheap to start, hard to forecast, and it discourages the frequent scanning that makes SAST useful.
- Platform bundle: SAST priced as part of a wider application security subscription with SCA, container, and sometimes AI security. Lower per-capability cost if you need more than one.
Most enterprise vendors in this list quote on request rather than listing prices; the free and open source options (Semgrep Community, SonarQube Community, OWASP tooling) set the floor. Mend.io’s current packaging is on our pricing page.
Notable SAST tools
Dedicated SAST tools
Here are the leading SAST solutions on the market, with their key features.
1. Mend.io
Mend SAST stops new vulnerabilities at the point of code creation. It delivers AI powered fixes and immediate feedback into the development workflow, including AI-assisted development, so developers resolve issues, human- or AI-written, as they appear.
Key features include:
- Cloud reporting with on-premises scanning: Keeps sensitive code private while enabling cloud-based reporting, quality gates, and workflow automation.
- AI coding agent integration: The Mend.io MCP server works with Cursor, Windsurf, and VS Code Copilot so generated code is checked and fixed before commit.
- Reduced noise and high precision: Pinpoints new vulnerabilities linked to recent changes, with 38% better precision and 48% better recall than benchmark competitors.
- AI powered fixes with every commit, 46% more accurate than competitors in an external test, so developers remediate without context switching.
- Near real-time feedback in the repo, with scans up to 10x faster than traditional SAST tools.
- 28 supported languages across Gen 2 and Gen 1 engines, with custom taint configuration per language.
2. Semgrep
Semgrep is a static analysis tool that identifies security issues with minimal noise by combining traditional static analysis with AI-based reasoning. It focuses on detecting real, exploitable vulnerabilities by understanding code context, developer intent, and application logic rather than relying only on pattern matching.
Key features include:
- Context-aware detection: Combines static analysis with AI reasoning to identify complex issues such as authorization flaws and business logic vulnerabilities
- Reachability-based prioritization: Uses code context and reachability analysis to highlight exploitable issues and reduce irrelevant findings
- Automated noise reduction: Learns from prior triage decisions to suppress recurring false positives and improve signal over time
- In-workflow remediation: Provides actionable fix guidance directly in pull requests, IDEs, and developer tools
- Workflow integration: Supports CLI, CI/CD pipelines, IDEs, and integrations with platforms like GitHub, GitLab, and Jira
3. SonarQube
SonarQube is a static analysis platform that combines security scanning with code quality and reliability checks, providing continuous inspection of codebases throughout development. It emphasizes early detection and remediation by integrating automated analysis into CI/CD pipelines and developer tools.
Key features include:
- Automated code analysis: Continuously scans code across branches, pull requests, and merges as part of the development pipeline
- Real-time developer feedback: Delivers immediate, actionable insights within IDEs and DevOps tools
- AI-powered remediation: Generates context-aware fix suggestions using AI to speed up issue resolution
- Standards-based detection: Applies predefined rules aligned with industry security and compliance standards
- Flexible deployment options: Available as both SaaS and self-managed deployments with support for on-premises and cloud environments
4. Checkmarx
Checkmarx is a SAST platform that focuses on identifying and prioritizing exploitable vulnerabilities within the development workflow. It emphasizes context-aware analysis to help developers understand which issues actually impact the application, reducing alert fatigue. The platform embeds security capabilities directly into IDEs and pipelines.
Key features include:
- Risk-based prioritization: Uses context and application security posture management to surface vulnerabilities that are truly exploitable
- In-IDE security integration: Embeds scanning and remediation guidance directly into developer environments to avoid context switching
- AI-assisted remediation: Provides code suggestions, explanations, and refactoring guidance to help fix issues securely
- Unified AppSec platform: Combines multiple security testing capabilities into a single system for visibility and coordination
- Scalable analysis: Supports large codebases and diverse technologies with flexible deployment and policy controls
5. Veracode
Veracode is a SAST platform focused on identifying and reducing application risk across the software development lifecycle. It combines static analysis with AI-driven insights to detect vulnerabilities at their root cause and prioritize remediation. The platform is designed to integrate into development workflows, helping teams continuously scan code, enforce security policies, and fix issues early with minimal manual configuration.
Key features include:
- Root cause analysis: Identifies underlying causes of vulnerabilities to support more effective remediation
- Lifecycle coverage: Applies security scanning and governance across all stages of the development process
- AI-assisted prioritization: Helps teams focus on critical risks by analyzing impact and exploitability
- Developer-centric guidance: Provides actionable recommendations within developer workflows
Evaluating other options? See our roundup of Veracode alternatives.
6. OpenText
OpenText static application security testing (formerly Fortify) is a SAST solution that detects vulnerabilities early while supporting enterprise-scale development and compliance requirements. It focuses on integrating security into DevOps processes and managing risk across complex environments. The platform is part of a broader ecosystem for secure information and application management.
Key features include:
- Early vulnerability detection: Identifies security issues during development to reduce downstream risk
- Enterprise integration: Connects with development and DevOps tools to embed security into workflows
- Scalable deployment options: Supports cloud, private cloud, and on-premises environments
- Compliance support: Aligns with governance and regulatory requirements across industries
- AI-assisted prioritization: Uses intelligent analysis to highlight critical vulnerabilities and reduce noise
7. Snyk Code
Snyk Code is a developer-focused SAST tool that emphasizes fast, in-context vulnerability detection and remediation. It performs static analysis without requiring full builds, allowing developers to identify and fix issues directly in their IDEs or pull requests. The platform uses a large knowledge base and machine learning models to provide accurate results and prioritize the most relevant risks based on application context.
Key features include:
- Real-time scanning: Analyzes code instantly in IDEs and pull requests without requiring builds
- Pre-validated auto-fixes: Provides tested remediation suggestions that can be applied directly in the workflow
- Context-aware prioritization: Focuses on newly introduced or exposed vulnerabilities to reduce noise
- Extensive knowledge base: Uses millions of data flow models and open source insights to improve detection accuracy
- Broad ecosystem support: Integrates with popular languages, IDEs, and CI/CD tools
Application security / DevSecOps platforms
8. Black Duck Software
Black Duck Software is an application security platform focused on managing software supply chain risk and securing development at scale. It integrates multiple security testing approaches into a unified system, helping organizations automate security checks and maintain visibility across the development lifecycle.
Key features include:
- Unified AppSec platform: Consolidates multiple security tools and signals into a single system for centralized risk management
- Supply chain security: Identifies and manages risks in open-source and third-party dependencies
- Automated security workflows: Embeds testing and risk detection across CI/CD pipelines without slowing development
- Enterprise risk visibility: Provides centralized insights and policy-driven prioritization across applications
- Support for AI-driven development: Secures code generated in modern development environments and pipelines
Looking for alternatives? See our guide to Black Duck alternatives.
9. HCL Software
HCL Software provides application security capabilities as part of a broader enterprise software portfolio that includes cybersecurity, DevOps, and AI-driven operations. Its SAST-related offerings focus on vulnerability detection, mitigation, and remediation across the software lifecycle, with an emphasis on operating at large scale in enterprise environments.
Key features include:
- Integrated cybersecurity capabilities: Combines vulnerability detection and remediation within a broader DevSecOps and enterprise security ecosystem
- High-throughput scanning: Supports large-scale code analysis, with reported capacity to scan significant volumes of code per hour
- Enterprise-scale deployment: Designed to operate across large organizations with extensive infrastructure and user bases
- AI-driven operations support: Aligns security analysis with AI-powered operational and automation capabilities
- Compliance and secure DevOps alignment: Emphasizes secure development practices and regulatory compliance across environments
10. GitHub Advanced Security
GitHub Advanced Security is a set of security features integrated directly into GitHub repositories, enabling developers to identify and remediate vulnerabilities within their existing workflows. It combines static analysis (via CodeQL and third-party tools) with dependency and secret scanning to provide comprehensive code security.
Key features include:
- Code scanning with CodeQL: Detects vulnerabilities and coding issues using GitHub’s native analysis engine or third-party tools
- Automated remediation: Provides generated fixes for security findings through features like Copilot Autofix
- Dependency review: Analyzes changes to dependencies and flags known vulnerabilities before merging
- Secret scanning and push protection: Detects and prevents exposure of sensitive credentials in code repositories
- Security visibility and governance: Offers organization-wide risk insights, campaigns, and automated triage rules
Best practices for using SAST tools
Here are some of the ways that organizations can improve their use of SAST tools.
1. Integrate where developers work
SAST tools are most effective when they meet developers where they write and review code. Embedding scans directly into IDEs and pull requests ensures that security checks happen in real time without interrupting workflows. This reduces the feedback loop, allowing developers to fix vulnerabilities before they move downstream, where remediation costs increase. Lightweight, incremental scans are preferable to heavy full-build analyses at this stage, as they provide fast and actionable results.
Integrating SAST into CI/CD pipelines is equally important to maintain DevOps speed. Security checks must run in parallel with build and deployment steps, not as blockers that slow delivery. A well-integrated SAST solution provides quick pass/fail signals, with detailed findings available for deeper inspection. This allows teams to maintain velocity while still enforcing consistent security guardrails at every stage of development. For a focused view on pipeline integration, see our guide to SAST tools for DevSecOps teams.
2. Prioritize with context
SAST findings can easily overwhelm teams if presented without prioritization. Contextual triage using exploitability, impact, and code relevance helps teams focus on vulnerabilities that matter and cut down on SAST false positives. Modern SAST tools can perform reachability analysis to determine if a flaw is actually exploitable within the application’s execution paths, reducing noise and false positives. This allows developers to concentrate effort on fixing issues that pose real security risks rather than chasing low-value alerts.
Stack awareness is another key factor in prioritization. A vulnerability that affects a critical service written in production languages should take precedence over an issue in a test harness or a deprecated component. AI-driven triage can automate this process by ranking vulnerabilities based on business-critical factors, ensuring that limited developer resources are spent on the flaws most likely to be exploited.
3. Accelerate remediation
Detection alone is insufficient if remediation lags. SAST tools should provide developers with AI-assisted fixes, code snippets, or precise guidance on where and how to patch issues. Automated remediation suggestions help reduce mean time to repair (MTTR) and ensure that fixes are aligned with the programming language and framework in use. This prevents wasted time on generic or inapplicable fixes that developers would otherwise need to adapt manually.
Autofix features can further accelerate remediation when combined with mandatory review steps. Developers receive proposed code changes that resolve vulnerabilities, which they can then validate and merge. This keeps control in the hands of engineers while eliminating repetitive manual patching. At scale, automated remediation workflows reduce backlog, improve consistency, and free up developer capacity for feature development. Autofix is also where AI code review tools overlap with SAST, so check how deep each one’s static analysis goes before treating it as a replacement.
4. Stay current with tech shifts
The programming landscape evolves quickly, and SAST tools must keep pace to remain relevant. Emerging languages like Rust, Dart, and Solidity introduce new security models and risks that older scanning rules may not detect. Similarly, AI frameworks such as LangChain, PyTorch, and TensorFlow bring unique attack surfaces, including prompt injection and model manipulation vulnerabilities. Organizations that fail to update SAST rules risk leaving critical blind spots in their coverage.
Staying current requires continuous updating of rule sets and vulnerability databases. Security teams should regularly review vendor updates, community rules, and new research on language-specific flaws. Some modern SAST platforms support dynamic rule delivery, ensuring tools are always aligned with the latest threats. By maintaining up-to-date coverage, organizations can proactively secure applications against both traditional vulnerabilities and new classes of risks driven by AI adoption and emerging technologies.
Coverage also stretches beyond application code. Infrastructure as code (IaC) files like Terraform and Kubernetes manifests carry their own misconfiguration risks, and IaC scanning usually runs as a separate scan type from SAST, so confirm how a vendor handles it.
5. Measure outcomes, not just scans
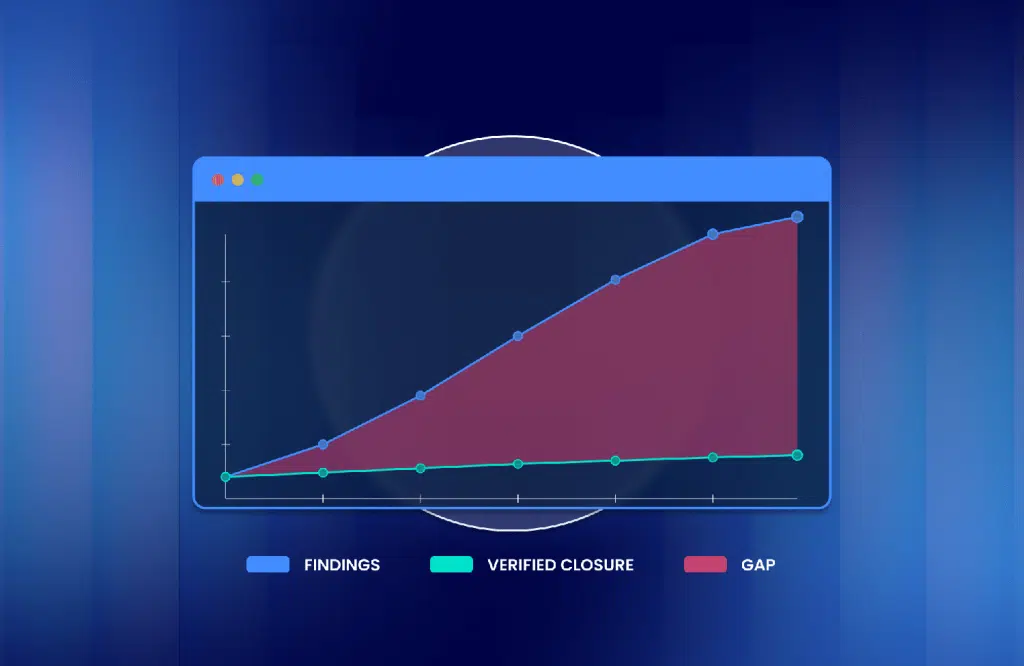
Running frequent scans is not enough—organizations must track whether vulnerabilities are actually being resolved. Metrics such as fix rates, mean time to repair, and developer adoption rates provide a clearer picture of real security improvements. For example, a high scan frequency with a low fix rate indicates that findings are not actionable or not being prioritized effectively. Tracking these metrics ensures that SAST programs deliver measurable outcomes instead of generating unused reports. Those metrics also give auditors evidence of secure development, which frameworks such as PCI DSS (Payment Card Industry Data Security Standard) expect.
Another key measure is scan latency in developer workflows. If pull request scans take too long, developers may bypass or resist the tool, reducing adoption. Large enterprises feel this most, since a slow scan repeats across every team and every pull request. Continuous monitoring of latency and feedback loops helps maintain usability. By focusing on outcome-driven KPIs rather than raw scan counts, organizations can avoid shelfware scenarios where tools are present but not delivering value. This ensures security investments align with business goals and development velocity.
Conclusion
SAST tools play a critical role in secure software development: early detection, integration into developer workflows, and actionable remediation guidance. Choose on your own evidence: run two candidates on the same repository, compare reachable findings rather than totals, time the pull request check, and confirm the languages you ship are on the vendor’s current engine.
FAQs
Which SAST tools support multiple programming languages?
Most tools here cover the mainstream languages (Java, JavaScript, Python, C#, Go), but coverage of legacy and mobile languages varies widely. Mend SAST lists 28 languages, including COBOL, ABAP, Apex, PL/SQL, Kotlin, and Swift, across two engine generations, and scans mixed-language repositories without separate configuration. Check each vendor’s current docs for the rest.
How much do enterprise SAST tools cost?
Enterprise SAST is priced per developer, per application, per scan, or as part of an application security bundle, and most vendors quote on request. The pricing model matters more than the list price: per-developer pricing rises with contractors and AI agents, per-application pricing with microservice sprawl. Mend.io publishes its packaging on its pricing page.
Which SAST tools integrate with IDEs and source control?
Most tools in this list integrate with GitHub pull requests; GitLab, Bitbucket, and Azure DevOps coverage varies. IDE integration now includes AI coding agents: Mend.io connects to Cursor, Windsurf, and VS Code Copilot through its MCP server so generated code is checked for CWEs before the developer accepts it, and reports differential scan results through GitHub, GitLab, Bitbucket Cloud, and Azure DevOps.
How do you choose a SAST tool that scales across large development teams?
Look for differential scanning so pull request checks stay fast on large repositories, baselining so existing findings do not flood new teams, policy and quality gates set centrally and applied per repository, and a pricing model that does not penalize growth. Mend SAST scans changed code at commit and reports up to 10x faster than traditional SAST tools.
What is the difference between SAST and AI code review?
SAST is deterministic analysis of source code for vulnerability patterns and taint paths; AI code review uses a language model to comment on a pull request, usually for quality and style. The strongest security results come from pairing them: a SAST engine to find the issue, AI to explain and fix it. Mend SAST works this way, with fixes 46% more accurate than benchmark competitors.