Secure how AI behaves, not just what it’s built from.
Cut through the noise to reduce real application risk.
Automated dependency updates, running on millions of repos.
Extend Mend AppSec to running apps, APIs, and aging dependencies.
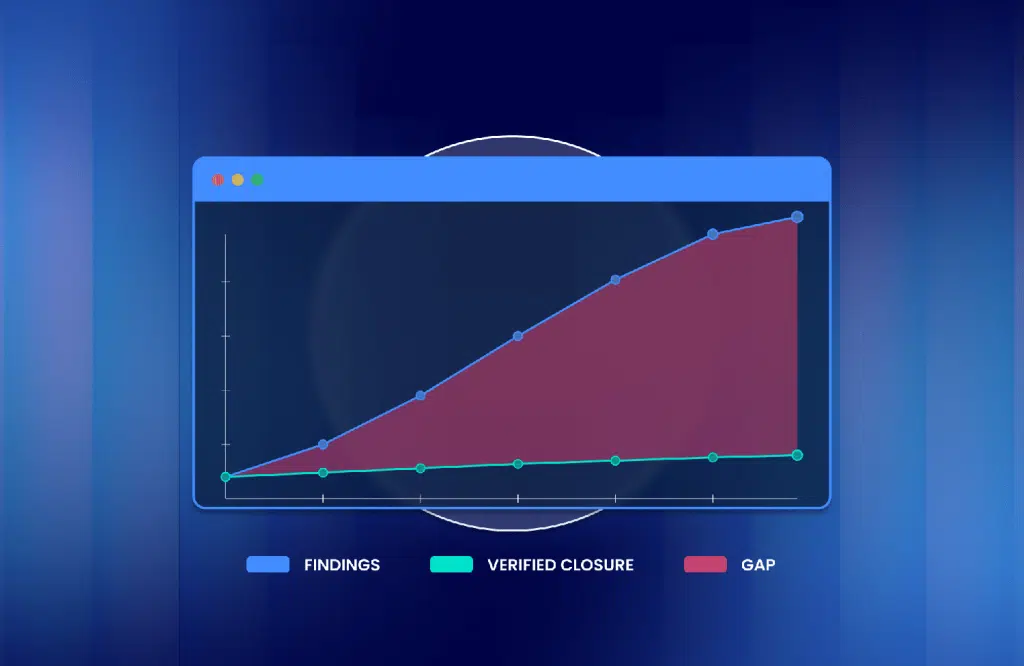
Top Open Source Vulnerabilities In 2026
Discover the top open source vulnerabilities in 2026.
npm vs Yarn in 2026: Which package manager should you choose?
npm vs Yarn in 2026: speed, security, and workspaces compared.
Top Black Duck Alternatives in 2026
Exploring the top Black Duck alternatives.
Comprehensive Guide to DevSecOps: Principles, Process, and Technology
Build secure software, faster. A complete guide to DevSecOps in practice.
Black Duck SAST Review: Pros, Cons and Technical Architecture
A detailed review of Black Duck SAST plus a Mend SAST alternative.
Introducing Mend.io’s AI Security Maturity Survey + Compliance Checklist available today
A new tool to help security teams quantify AI risk and prepare for 2026 regulations.
Best Software Composition Analysis for Enterprise: Top 8 in 2026
Explore this guide to the best software composition analysis tools for large teams.
LLM Red Teaming: Threats, Testing Process & Best Practices
A practical guide to LLM red teaming.
Black Duck SCA: Pros/Cons, Architecture, and Quick Tutorial
A detailed review of Black Duck SCA plus a Mend SCA alternative.
Best practices for dealing with Log4j in 2026
Log4j best practices for 2026: sanitize input, scan dependencies, stay patched.
Understanding Veracode SAST: Pros/Cons, Architecture, and Pricing
A detailed review of Veracode SAST plus a Mend SAST alternative.
Veracode SCA Solution Overview: Features, Limitations, and Tutorial
A detailed review of Veracode SCA plus a Mend SCA alternative.
Mend.io Leadership Update: Building on Our Momentum for the Next Phase of Growth
An update on Mend.io’s leadership as we enter the next phase of growth.
Why AppSec and Network Risk Management Must Be Unified in the Modern Enterprise
See how Mend.io’s ServiceNow integration unifies application, network, and operational risk.
NPM User Flooding Registry with Fake Font Packages
Analysis of an npm account flooding the registry with malformed font packages.
MCP Security: 10 Key Elements to Secure and Critical Best Practices
Learn what MCP security is, key risks like prompt injection, and best practices.
Never miss a post. Opt-out at any time.
You’re all set to receive our latest posts.