Table of contents
Related resources


AI code review tools: Key benefits and 8 tools to know in 2026

What are AI code review tools
AI powered code review tools analyze source code to find bugs, security vulnerabilities, and performance problems before they reach production. They scan codebases, pull requests, and commits, suggest improvements, and flag the areas that need attention. AI coding assistants such as GitHub Copilot and OpenAI Codex are not AI code review tools, even though teams often use them that way.
These tools plug into development environments and continuous integration pipelines, so reviews run faster with fewer missed issues. As codebases grow and release cycles shorten, AI code review tools help teams keep up with changing standards, surface hidden flaws, and hold code quality steady.
AI first IDEs like Cursor raise the stakes. Human reviewers can’t match the pace of AI-generated code, and reviewing it well is harder than reviewing code a colleague wrote. Automated review is the only way to keep pace.
If security is your main concern, see our comparison of AI code review tools for vulnerability detection, which goes deeper on SAST, SCA, and noise reduction.
This is part of a series of articles about SAST.
Key benefits of AI code review tools
AI code review tools improve software quality by automating and extending code analysis, so teams deliver better code with less effort. The main benefits:
- Better code quality: AI tools detect issues in logic, readability, security, and maintainability. They go beyond syntax checks with context-aware recommendations that help developers write cleaner, more reliable code.
- Less manual effort: Automated reviews cut the time spent on routine inspection. Reviewers focus on critical logic and design decisions while the tool handles the rest.
- Faster feedback: Instant feedback during development or CI runs catches errors early. Developers don’t wait for a peer review to find basic issues.
- Consistency: AI enforces coding standards uniformly across the codebase, which keeps style and structure coherent and maintainable.
- Lower risk: Catching security flaws and bugs early reduces production incidents and keeps code aligned with best practices and industry standards.
Advanced code review tools add the following:
- Semantic error detection: Finds logical flaws that traditional linters miss, such as incorrect iteration patterns, missing edge cases, or flawed conditional logic.
- Test coverage feedback: Suggests missing test cases by analyzing changes in code behavior or input handling.
- Risk-based prioritization: Integrates with security review tools to flag vulnerabilities and weaknesses, so teams work on high-impact issues first.
- Contextual review: Asks targeted questions in pull requests that prompt deeper thought about design choices.
- Foundation for governance: Reviews code against organizational policies for security, performance, and documentation, which supports long-term compliance and maintainability.
Read our detailed guide to AI code review.
Notable AI code review tools
1. Mend.io
Main focus: Application Security review built into the SDLC
Mend.io brings security into every code review. Mend SAST, the static analysis component of Mend AppSec, scans source code whether a developer or an AI assistant wrote it, and finds vulnerabilities and hardcoded secrets across the repository and the IDE. Mend SCA covers the open source dependencies alongside it, with reachability analysis that tells you whether your code can actually execute a vulnerable function. Findings and fixes land in pull requests and CI/CD pipelines, so teams catch issues early and ship without slowing down.
Key features include:
- Scanning at the point of generation: Connects to AI first IDEs such as Cursor, Windsurf, and Copilot, so AI-generated code is checked as it is produced and again at commit.
- Incremental scanning: Analyzes only the code that changed between scans and runs up to 10x faster than traditional SAST solutions.
- AI powered code fixes: Generates suggested fixes in the repository that are +46% more accurate than the average competitor in an external third-party test.
- Accuracy: Delivers +38% precision and +48% recall versus benchmark competitors, which means fewer false positives for reviewers to triage.
- Dependency risk analysis: Identifies and prioritizes open source vulnerabilities and license issues by reachability.
For a closer look at how Mend.io compares with other security-focused review tools, read our guide to AI code review tools for vulnerability detection.

2. SonarQube
Main focus: Quality gates and governance
SonarQube is a static analysis and code review tool that analyzes code written by developers and AI across 35 languages. It improves code quality, enforces security standards, and gives developers immediate feedback through IDE and CI/CD integration. An MCP server connects AI coding agents to its analysis, and an AI Code Assurance workflow gives AI-generated code its own review path.
Key features include:
- Automated code analysis: Performs static analysis on every code change and identifies bugs, vulnerabilities, and maintainability issues.
- Real-time feedback: Delivers findings inside IDEs and pull requests.
- Security compliance: Checks code against standards such as OWASP Top 10, CWE Top 25, and PCI DSS.
- Quality gates: Blocks merges when code fails defined quality and security thresholds.
- Reporting: Provides dashboards and metrics to monitor code health and track trends.

Source: SonarQube
3. CodeRabbit
Main focus: Conversational AI for pull requests
CodeRabbit is an AI code review platform that automates line-by-line reviews in pull requests and IDEs. Built for GitHub, GitLab, and Azure DevOps, it combines static analysis tools, configurable AI review logic, and feedback learning to catch bugs and improve code quality.
Key features include:
- Line-by-line AI reviews: Analyzes each change with awareness of the broader codebase to catch subtle issues.
- Configurable review behavior: Lets teams tune review style and depth with feedback loops and written instructions.
- Code change summaries: Generates one-line descriptions of file changes and concise PR summaries.
- Integrated chat agent: Offers conversational help for writing code, resolving comments, generating docstrings, and managing tasks.
- Signal-focused analysis: Combines static analyzers, linters, security tools, and generative AI with code graph context.
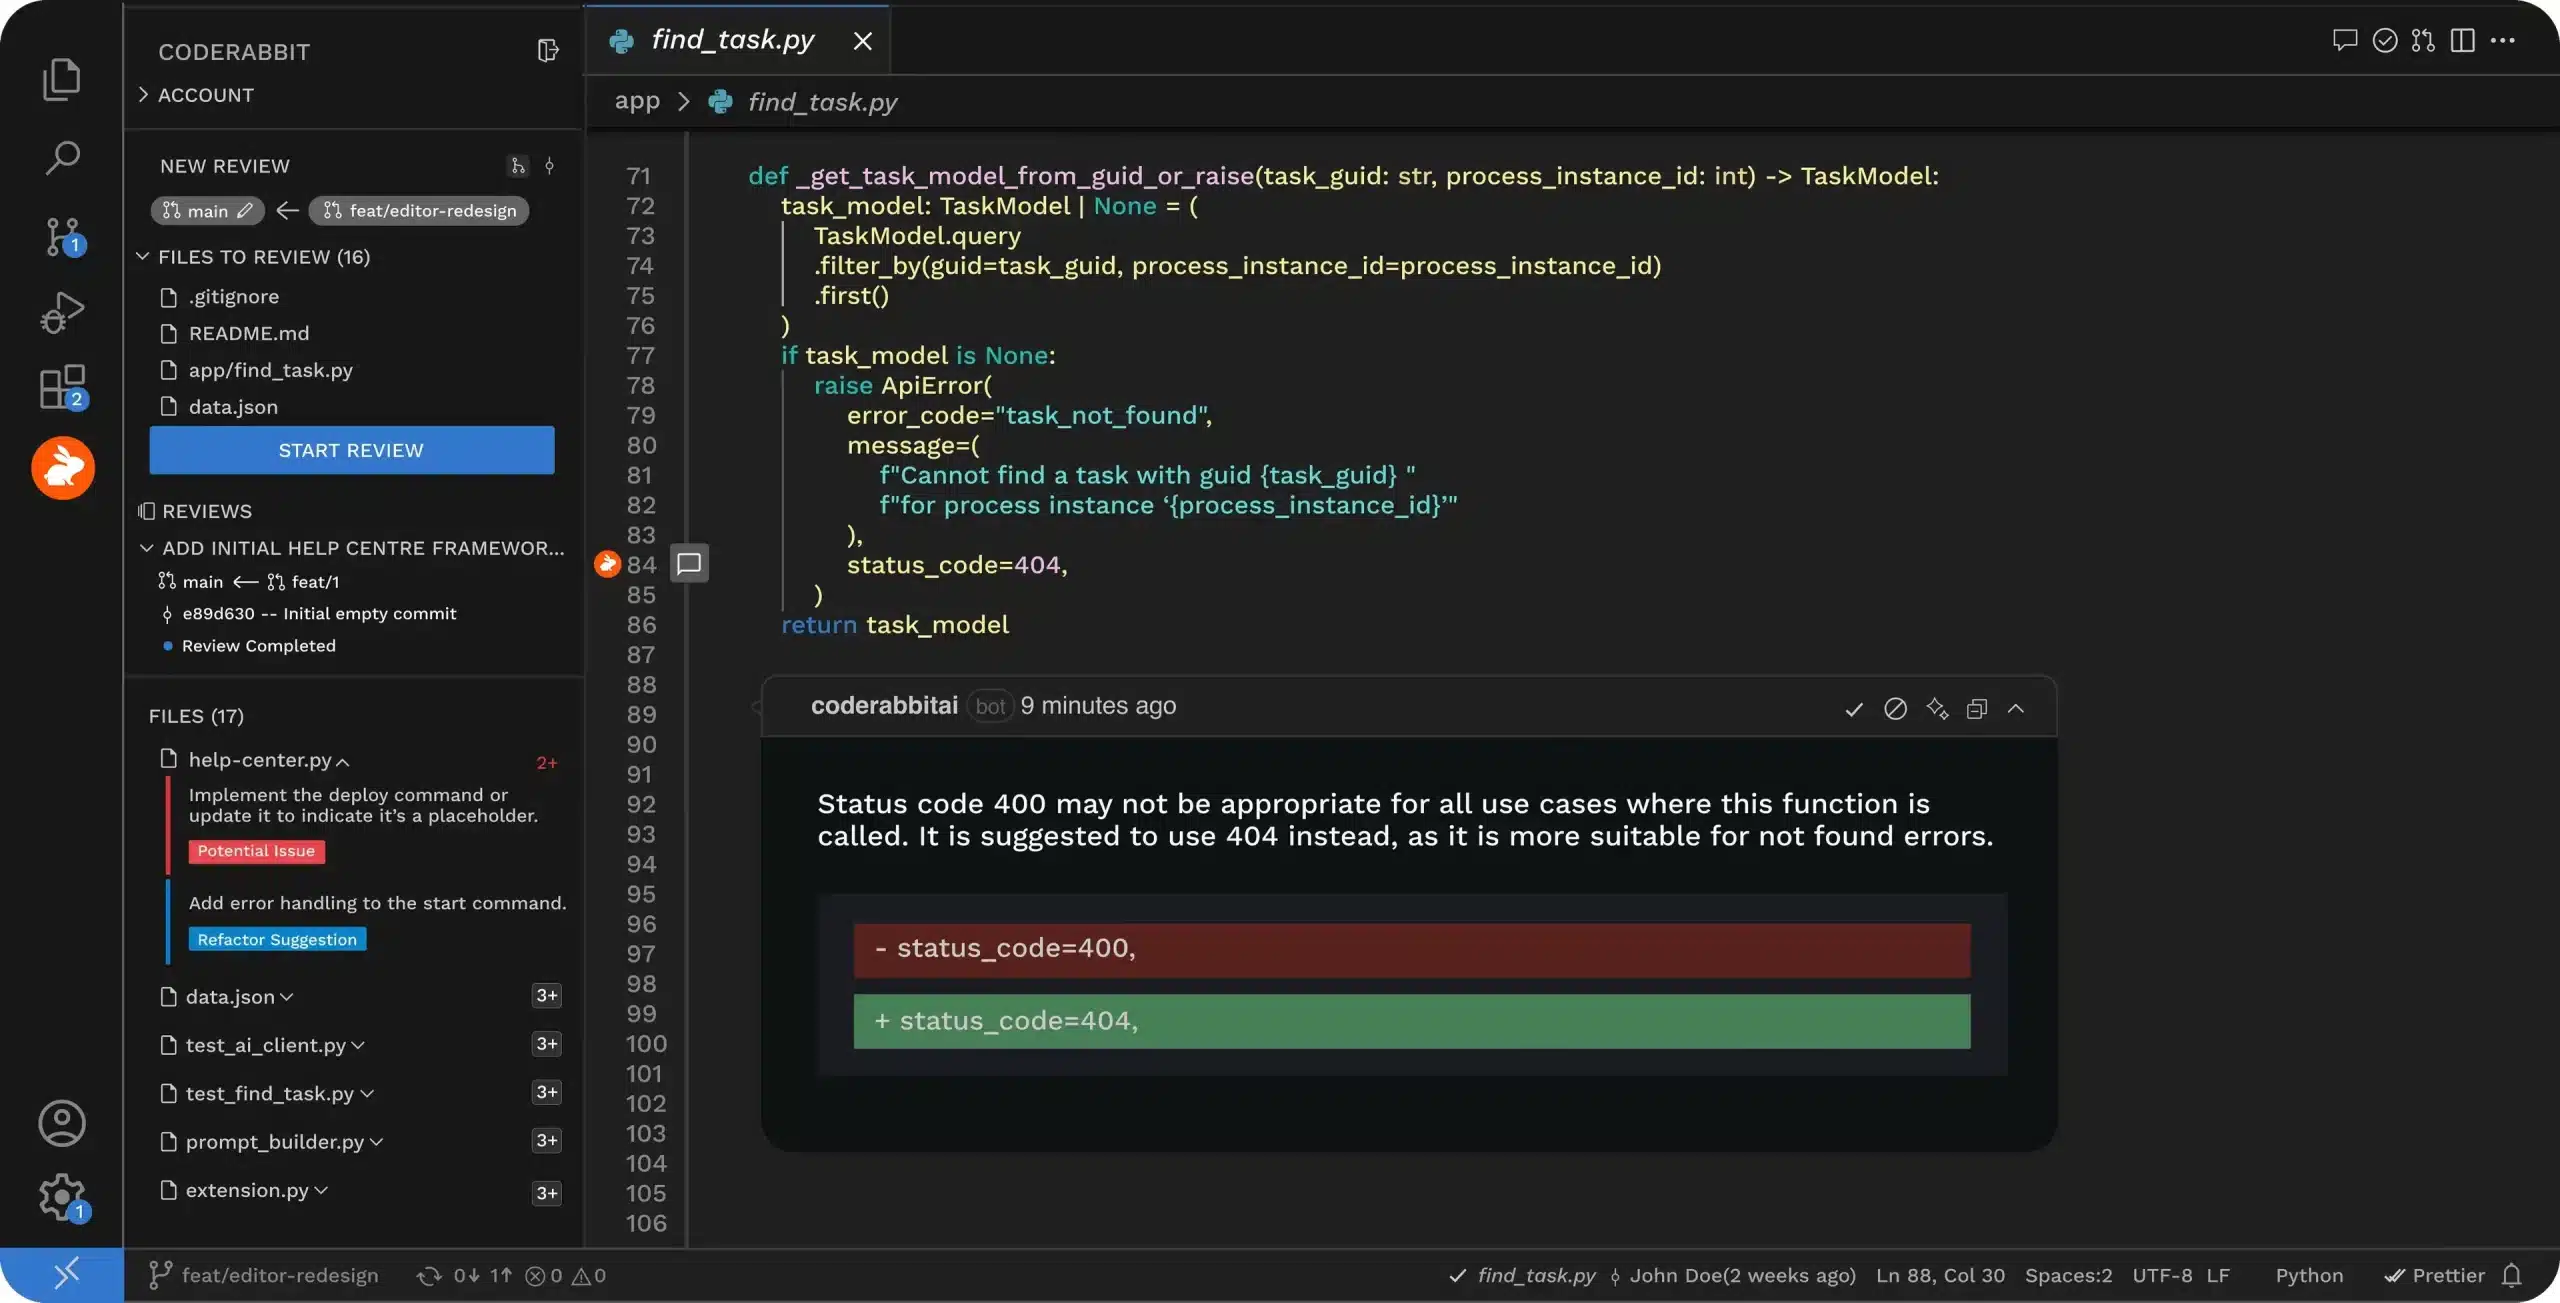
Source: CodeRabbit
4. CodeScene
Main focus: Behavioral code analysis and hotspots
CodeScene is an AI-augmented code review tool that protects code health and prevents technical debt. It automates pull request reviews with customizable quality gates aligned to team goals, so only code that meets the bar gets merged.
Key features include:
- Automated code health checks: Reviews every pull request against defined Code Health rules so new code maintains or improves quality.
- Technical debt detection: Spots early signs of code degradation before debt accumulates.
- Configurable quality profiles: Offers built-in review strategies such as “Pay Down Technical Debt” or “Clean Code Collective,” plus custom profiles.
- Context-aware review gates: Adjusts quality bars by repository section, team, or project scope.
- Trend monitoring: Tracks code health and developer adoption across sprints and shows the effect of each pull request on maintainability.

Source: CodeScene
5. Snyk Code
Main focus: Security-centric pull request insights
Snyk Code is the SAST product in Snyk’s developer security platform. Its DeepCode AI engine combines symbolic and generative AI with machine learning models trained on more than 25 million data flow cases across 19 languages. The engine powers Agent Fix, which generates code fixes, and context-aware risk scoring that ranks findings by package popularity, reachability, and exploit maturity.
Key features include:
- DeepCode AI engine: Uses a hybrid of symbolic and generative AI to detect and prioritize vulnerabilities in source code.
- Agent Fix autofixes: Delivers developer-ready code patches for common security issues.
- Multi-model security intelligence: Employs specialized AI models trained on vetted security datasets.
- Data privacy by design: Does not train on customer data.
- Risk-based prioritization: Surfaces the most critical risks first using popularity, reachability, and exploit maturity.

Source: Snyk
6. Qodana
Main focus: JetBrains native AI code reviewer
Qodana is a static code analysis platform from JetBrains that brings the inspection capabilities of its IDEs into CI pipelines. It supports over 2,500 inspections out of the box and integrates with JetBrains IDEs and popular CI tools.
Key features include:
- JetBrains-powered analysis: Uses the same static analysis engines as JetBrains IDEs for consistent results locally and in CI.
- IDE and CI integration: Keeps inspections aligned between the developer’s IDE and the build pipeline.
- Automated quick-fixes: Suggests fixes developers can apply from the IDE or CI output.
- Inspection set: Includes over 2,500 checks for bugs, performance issues, style violations, unused code, and naming conventions.
- Security and license compliance: Detects vulnerable dependencies and incompatible third-party licenses.

Source: JetBrains
7. Codacy
Main focus: Continuous code quality for teams
Codacy is a code quality and security platform aimed at AI-assisted development teams. It lets teams define standards once and enforce them across projects, combining SAST, SCA, secrets detection, and IaC scanning with AI policy checks. Its AI Reviewer gives low-noise pull request feedback, and Codacy Guardrails checks AI-generated code against policies as it is created.
Key features include:
- AI Guardrails: Checks AI-generated code against policies as it is written.
- IDE and AI agent integration: Connects with developers’ IDEs and AI tools to deliver feedback during coding.
- AI Reviewer: Delivers pull request feedback with fix suggestions, summaries, and automatic false-positive detection.
- Centralized policy management: Applies consistent security and quality rules across repositories, projects, and teams.
- Compliance reporting: Generates SBOMs and supports SOC 2 and ISO frameworks.

Source: Codacy
8. Qodo
Main focus: Agentic pull request review with test generation
Qodo is an AI code review platform that works across the IDE, pull requests, the CLI, and Git. Its agentic pull request review gathers context from multiple repositories, pull request history, and linked tickets, then uses specialized agents to find issues and rank them by severity so blockers surface first.
Key features include:
- Agentic PR review: Uses specialized agents to find and prioritize issues in pull requests.
- Context engine: Gathers context from multiple repositories, pull request history, and tickets.
- Implementation-ready prompts: Produces prompts that pair issue context with code ranges for an AI coding assistant.
- Rules enforcement: Generates and enforces rules derived from organizational and historical context.
- Requirement validation: Checks code against the requirements in linked tickets.

Source: Qodo
Considerations for choosing AI code review tools
Picking the right tool takes more than a feature comparison. The tool has to fit your workflow, match your security posture, and support your programming ecosystem. Weigh the following:
- Integration: The tool should connect with your version control system, CI/CD pipeline, and IDE, so developers get feedback without changing how they work.
- Specific needs: Match the tool’s strengths to your primary review goal, whether that is detecting security vulnerabilities, improving performance, or enforcing maintainability standards.
- Cost: Consider per-user fees, repository-based pricing, or enterprise packages, plus long-term scalability and hidden costs for advanced features.
- Learning curve: Evaluate how quickly your team can adopt the tool. Shorter onboarding means earlier adoption and less disruption.
- Code focus: Decide whether reviews target performance-critical hot paths or mostly glue code. That determines whether you need deep performance analysis, maintainability checks, or both.
- Developer trust: Gauge how comfortable your team is with automation. If there is resistance, choose tools with explainable output, low false-positive rates, and clear justifications.
- Noise reduction: Check whether the tool learns from past reviews and adapts to your team’s coding style, so repetitive or irrelevant findings fade over time.
- Workflow compatibility: Confirm the tool fits your existing pull request and review process instead of adding disruptive new steps.
- Domain-specific rules: Make sure the tool supports custom rules for your product’s security, compliance, or business logic requirements.
Conclusion
AI-assisted code review multiplies software quality, but only when it fits both the technical demands of the codebase and the human factors of the team. The best tools balance accuracy with adaptability, automate without overstepping, and slot into established workflows rather than replacing them. Chosen well, they help teams catch more issues earlier, hold higher standards, and move faster with confidence.