Secure AI powered applications
AI models and agents are transforming your apps and introducing new risks that traditional AppSec tools can’t handle. Mend AI can help.

Challenges
AI risks are unlike anything security teams have faced
They’re dynamic, unpredictable, and largely invisible to existing application security tools.

Lack of visibility
Most AppSec tools cannot identify AI models, agents, RAG pipeline, and MCP servers in your apps. How can you manage what you don’t know you have?
Unpredictable behavior
AI components evolve, behave non-deterministically, and respond unpredictably to malicious prompts.
Compliance blind spots
AI introduces new licensing, regulatory, and compliance challenges, without standardized ways to govern or track them.
Opportunities
Secure AI powered apps with confidence
Take a proactive approach to addressing these risks, with new tools purpose-built for AI systems.

Map every AI component
Automatically detect AI models, agents, RAGs, and MCPs in your applications, and build a live, continuously updated AI-BOM.
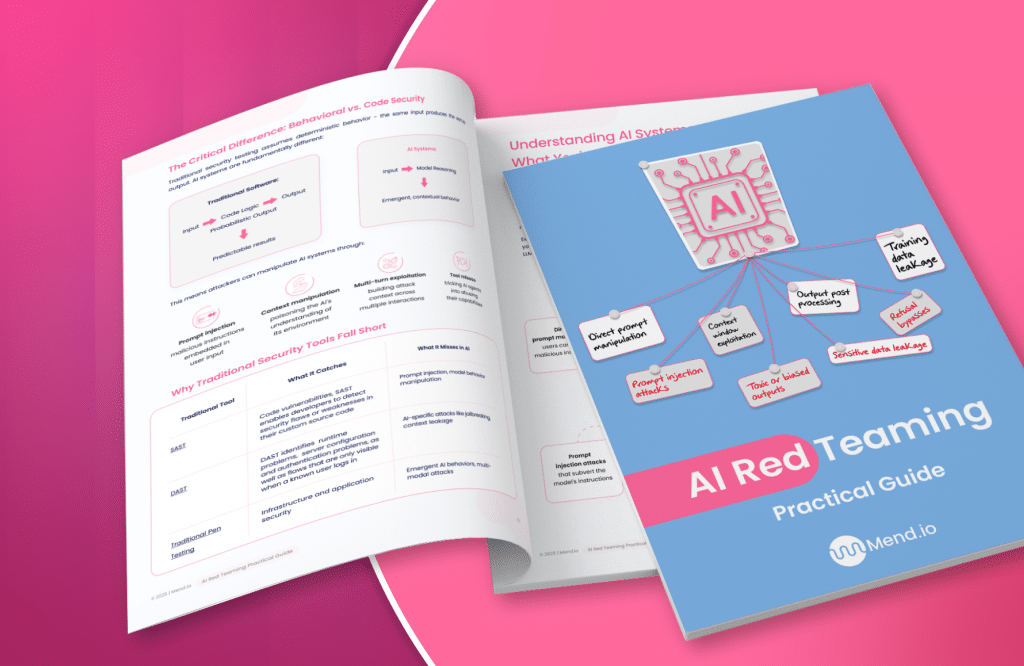
Simulate adversarial behavior on AI
Run adversarial simulations to uncover how your conversational AI is behaving to uncover jailbreaks, hallucinations, bias, data leaks, and more.
Enforce policies at scale
Apply rules for model usage, licensing, and prompt safety, with automated enforcement and approval workflows.
The solution
Mend AI
Mend AI tests against threats like prompt injection, context leakage, and data exfiltration to uncover AI behavioral risks unique to your application.

Discover Mend AI


“One of our most indicative KPIs is the amount of time for us to remediate vulnerabilities and also the amount of time developers spend fixing vulnerabilities in our code base, which has reduced significantly. We’re talking about at least 80% reduction in time.”


“When the product you sell is an application you develop, your teams need to be fast, secure and compliant. These three factors often work in opposite directions. Mend provides the opportunity to align these often competing factors, providing Vonage with an advantage in a very competitive marketplace.”


“The biggest value we get out of Mend is the fast feedback loop, which enables our developers to respond rapidly to any vulnerability or license issues. When a vulnerability or a license is disregarded or blocked, and there is a policy violation, they get the feedback directly.”


FAQs
How does Mend.io secure AI powered applications?
Mend AI discovers and inventories AI components, identifies risks in models, system prompts, and agent configurations, tests application behavior through adversarial simulations, and enforces guardrails on AI inputs and outputs, all within existing security workflows.
What does Mend AI cover that traditional AppSec tools miss?
AI-specific risk beyond SAST and SCA. Mend AI analyzes system prompts and agent configurations, tests how AI powered applications respond to adversarial inputs, and inspects runtime inputs and outputs for threats such as prompt injection, jailbreaks, sensitive-data exposure, exposed secrets, and harmful content.
For threat types and best practices, read the AI application security guide.
How does Mend.io discover AI components in my codebase?
Mend AI scans application code and package inventories to identify AI technologies, frameworks, models, and inference providers (including shadow AI added without security review) and builds a live, continuously updated AI-BOM.
Can Mend.io test AI applications for behavioral risks?
Yes. Mend AI Red Teaming runs configurable adversarial simulations against AI powered applications using prebuilt templates and customizable tests. It helps uncover application-specific risks such as prompt injection, jailbreaks, context leakage, data exfiltration, harmful behavior, and other weaknesses that only appear when the AI system is interacting with users and data.
How does Mend.io enforce AI security policies across teams?
Mend AI uses policy-driven automation workflows to govern AI components, identify violations, and apply consistent security and licensing standards throughout development. At runtime, centrally configured guardrails inspect AI inputs and outputs and can alert, block, or obfuscate content based on the detected risk and organizational policy.