
Mend SAST
The SAST tool that moves at AI speed
A vulnerability caught in the IDE (integrated development environment) takes a few minutes to fix. The same vulnerability caught in production can take days to fix, or worse, cause a breach. AI assistants write code just as fast as they introduce risk, and most SAST tools can’t keep up, burying real findings in so many false positives that developers stop trusting the results. Mend SAST finds real vulnerabilities in human- and AI-generated code, cuts the noise with agentic triage, and uses AI to hand developers a fix they can apply in minutes, matching the speed AI set in the first place.




Why Mend.io
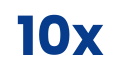
faster scans than legacy SAST tools
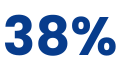
better precision than the competition
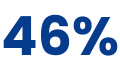
more accurate fixes than the competition
Feed agentic IDEs what they need to self-fix, pre-commit
Find and fix code flaws before they reach the repo, whether a developer wrote the code or Copilot did. Mend SAST feeds findings straight into Cursor, Windsurf, and Copilot, so the fix happens inside the same workflow that wrote the code.

Cut noise before it becomes developer work
Most SAST tools force a tradeoff: catch more vulnerabilities and drown developers in false positives, or cut the noise and miss real risk. Mend SAST starts with 38% better precision and 48% better recall than benchmark competitors, then runs agentic triage on top to explain which findings are worth a developer’s time. Less digging, more fixing.

Turn findings into fixes before production
Every finding comes with an AI-based fix that’s 46% more accurate than benchmark competitors, and ready to review in the pull request. Less time spent researching a patch, more time spent shipping it.

Keep security feedback moving at AI speed
Mend SAST scans up to 10x faster than legacy SAST tools, checking only what changed instead of re-scanning the whole repo. When AI assistants write a feature in minutes, security can’t be the two-day wait that follows it.

Govern code security without sending source code to the cloud
Scan on premises or inside your own environment, so proprietary code never leaves your perimeter. Findings, policies, and dashboards still run in the Mend.io cloud, so you get SaaS (software as a service) visibility without handing over your IP.

What slow SAST costs your team

By the time a slow scan flags a flaw, the author is working on something else. Fixing it means reloading the old code and retesting around newer commits.

Teams often move SAST into a separate continuous integration (CI) job so long scans don’t block builds. Findings then arrive after the merge, so the fix needs a follow-up pull request.

When a scan threatens a release date, someone skips it. That code ships unscanned.

A developer using Copilot or Cursor can generate several changes before a multi-hour scan returns its first result.

A one-line patch can trigger a full re-scan before anyone knows whether it worked.

A critical flaw found days before launch pulls developers off planned work to rewrite code under pressure.
Fits the stack you already have
Mend SAST integrates natively with the IDEs, repos, and CI/CD (continuous integration/continuous delivery) tools your team already runs, including GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, and VS Code. Scans run straight from your repository, no build step required, and support for 30+ languages means one scanner covers your whole codebase.

Explore Mend SAST, part of Mend AppSec
Secure custom code with AI powered fixes, delivered in the repo.

Learn more about how we can help

Continuously detect and prevent code flaws before deployment.

Receive on-demand differential results without context switching.

Secure AI generated code without slowing down development.
Trusted by security teams all over the world


If we look at the number of PRs created by Mend SCA that were merged and compare that to the cost of developers doing that manually, then we have saved considerable developer time.


One of our most indicative KPIs is the amount of time for us to remediate vulnerabilities and also the amount of time developers spend fixing vulnerabilities in our code base, which has reduced significantly. We’re talking about at least 80% reduction in time.


When the product you sell is an application you develop, your teams need to be fast, secure and compliant. These three factors often work in opposite directions. Mend provides the opportunity to align these often competing factors, providing Vonage with an advantage in a very competitive marketplace.


The biggest value we get out of Mend is the fast feedback loop, which enables our developers to respond rapidly to any vulnerability or license issues. When a vulnerability or a license is disregarded or blocked, and there is a policy violation, they get the feedback directly.
Mend SAST FAQs
What is Mend SAST?
Mend SAST is a static application security testing tool that secures human- and AI-generated code with high-accuracy static analysis, Agentic SAST triage, contextual risk prioritization, and automated remediation. It helps teams identify real vulnerabilities, understand which risks matter most, and fix them directly within developer workflows. Mend SAST is included in Mend AppSec.
How does Mend SAST scan up to 10x faster than traditional SAST tools?
Mend SAST uses incremental, differential scanning that analyzes only changed code rather than re-scanning the entire repo on every commit. Combined with high-performance scans that run on commit and use intelligent syntax and data flow analysis. This delivers results 10x faster than legacy SAST — fast enough to keep up with AI-paced development.
How does Mend SAST reduce false positives?
Mend SAST starts with highly accurate detection, delivering 38% better precision and 48% better recall than benchmark competitors. Agentic SAST triage then analyzes findings using code and data-flow context to assess true- and false-positive likelihood, providing an explanation for each assessment. This reduces manual investigation and helps teams focus on findings that require action.
Can Mend SAST scan AI-generated code from Copilot, Cursor, and similar tools?
Yes. Mend SAST is built for AI-driven development: a lightweight scan runs at the moment of code generation in the IDE, with deep static analysis at commit. This catches vulnerabilities in AI-generated code before it lands in the repo, with AI-powered fixes that are 46% more accurate than competitors.
Does Mend SAST include secrets scanning?
Yes. Mend SAST detects hardcoded credentials, API keys, tokens, and certificates. Detected secrets trigger automated policy violations and can fail the build, preventing exposed secrets from reaching production.
How many programming languages does Mend SAST support?
Mend SAST supports 30+ programming languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++. Coverage spans web, mobile, server-side, and infrastructure-as-code languages used in modern AI-native applications.
Does Mend SAST require uploading source code to the cloud?
No. Mend SAST performs scanning on-premises or inside your own environment, so proprietary source code never leaves your perimeter. Findings, dashboards, and policy management run in the Mend cloud — giving you SaaS convenience without sacrificing IP confidentiality, ideal for regulated and high-IP industries.
How does Mend SAST integrate with IDEs and CI/CD pipelines?
In the IDE, Mend SAST supports JetBrains, VS Code, and Visual Studio, plus agentic IDEs such as Cursor and Windsurf, so developers see findings and AI powered fixes while they code. In the repository, it connects to GitHub, GitLab, Bitbucket, and Azure DevOps to scan each commit and surface fixes in the pull request. In the pipeline, it runs in Jenkins, CircleCI, GitHub Actions, and other CI/CD systems, so developers never have to leave the tools they already use.
How does Mend SAST prioritize vulnerabilities?
Mend SAST goes beyond severity by combining finding-level security evidence with application context. Contextual Project Classification analyzes characteristics such as sensitive data and critical functionality and surfaces project risk factors that help security teams determine which applications and findings warrant attention first.
How does Mend SAST compare to Snyk Code or GitHub Advanced Security?
Snyk Code and GitHub Advanced Security both scan code you write. Mend SAST does too, and adds agentic triage that explains why a finding is a true or false positive, AI-generated fixes that are 46% more accurate than benchmark competitors, and on-premises scanning that keeps source code off third-party servers. GitHub Advanced Security ties you to GitHub’s ecosystem. Mend SAST works the same way across GitHub, GitLab, Bitbucket, and Azure DevOps.
What are the key features of Mend SAST?
Mend SAST combines high-accuracy static analysis, agentic triage, Contextual Project Classification, AI-based remediation, and support for AI coding assistants like Copilot and Cursor. It scans up to 10x faster than legacy tools, delivers 38% better precision and 48% better recall than benchmark competitors, detects hardcoded secrets, scans on-premises, and integrates natively with 30+ languages and the tools your team already uses.
Does Mend SAST integrate with GitHub Actions, GitLab CI, and Azure DevOps?
Yes. Mend SAST runs as a pipeline step in GitHub Actions, GitLab CI, and Azure DevOps, as well as Jenkins and Bitbucket. Because it scans only the code that changed, it’s fast enough to run on every pull request. Policies set in the Mend.io cloud can fail the build when a finding breaks a rule, such as a hardcoded secret, and the suggested fixes appear in the pull request for review.
Does Mend SAST map to OWASP Top 10?
Yes. Mend SAST detects the vulnerability classes in the OWASP Top 10, including injection flaws, broken access control, and security misconfiguration, and adds the context needed to prioritize which ones to fix first.
Does Mend SAST help with compliance frameworks like PCI-DSS, HIPAA, or SOC 2?
Yes. On-premises scanning and audit-ready findings help teams meet the source-code security controls required by PCI-DSS, HIPAA, and SOC 2, without slowing development down to prepare for an audit.
Explore SAST resources

Stop managing alerts.
Start reducing risk.
Join the teams reducing remediation effort by 75%.