Secure how AI behaves, not just what it’s built from.
Cut through the noise to reduce real application risk.
Automated dependency updates, running on millions of repos.
Extend Mend AppSec to running apps, APIs, and aging dependencies.
Mend.io upgrades 184 open source organizations to the Renovate Community (OSS) plan
184 open source organizations now have the Renovate Community (OSS) plan
NIST SSDF: 4 core practices for secure software development
What the NIST SSDF requires and how to implement its four practice groups.
What Is AI Governance? A Practical Framework for Security Teams
How security teams turn AI governance into an operational practice.
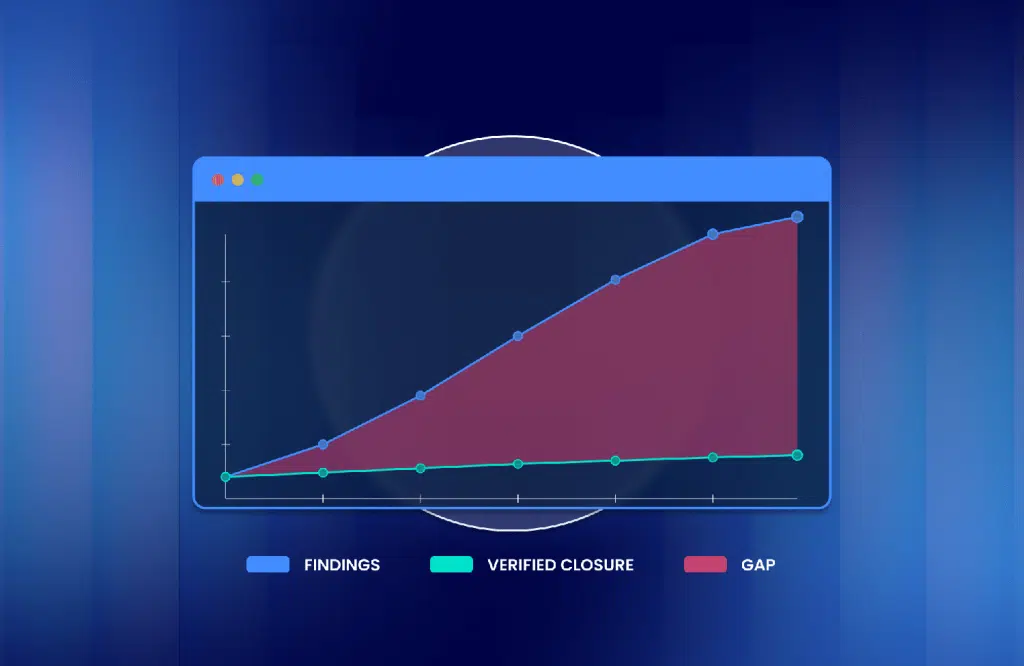
Detection scaled. The loop did not.
Findings got cheap. Verified closure did not. That gap is the AppSec problem.
Mend Renovate Enterprise: managing dependencies at agentic scale
How Mend Renovate Enterprise keeps dependency updates flowing at agentic scale.
Mini Shai-Hulud hits openapi-react-query-codegen: 10 malicious npm versions
An npm supply chain attack published ten malicious versions
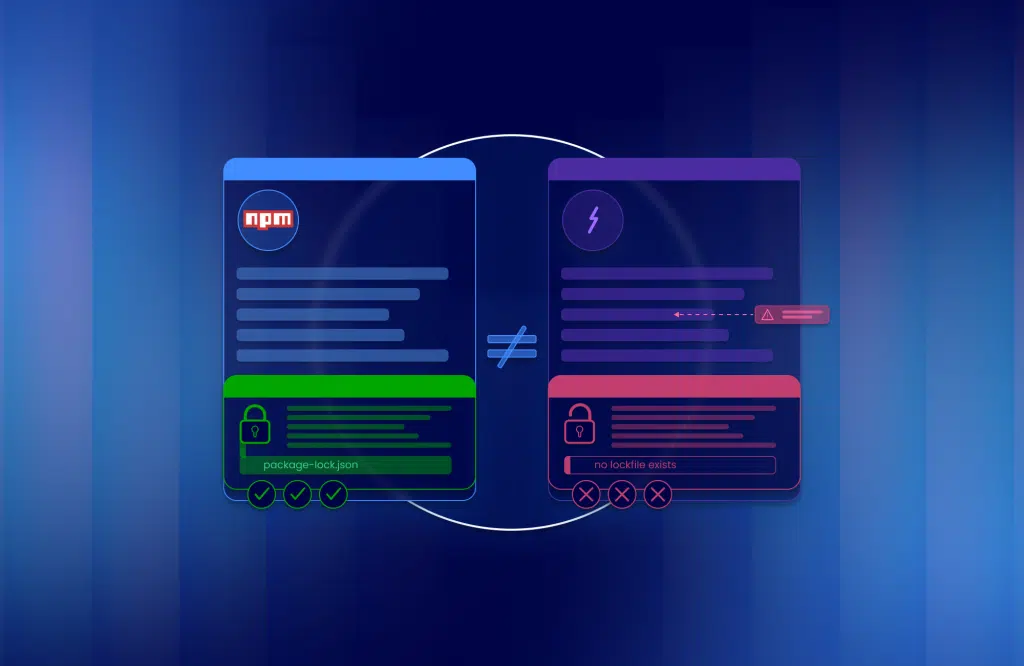
The skill layer is a dependency problem without a lockfile: what the OWASP Agentic Skills Top 10 gets right
Nine solved supply chain risks, one new gap: the OWASP Agentic Skills Top 10.
OWASP LLM Top 10 2026: the model will be fooled, the question is what breaks
The 2026 OWASP LLM Top 10 shifts the job from prevention to containment.
EU AI Act: risk tiers, timeline, and compliance requirements
Risk tiers, deadlines, and compliance steps under the EU AI Act.
That’s a wrap: Mend.io at Black Hat USA 2026
Mend.io at Black Hat USA 2026: keynote, podcasts, awards, and a hit booth game.
Patch faster isn’t the answer. Patch smarter is.
AI killed the patch window. Smarter patch management is how teams keep up.
Mini Shai-Hulud Hits keyv: Trojanized Release Exfiltrates CI Secrets via GitHub
Trojanized keyv@6.0.0 exfiltrates CI secrets through GitHub’s own API.
EU CRA explained: requirements, timeline, and compliance
What the EU CRA requires, key deadlines, penalties, and how to comply.
Move faster than AI-driven risk: Inside Mend.io’s latest AI application security update
AI agent discovery, runtime guardrails, agentic triage, and zero-day speed.
Top 13 AI security testing solutions for dev pipelines in 2026
Compare the top AI security testing solutions for dev pipelines.
199 RubyGems, two techniques, zero working payloads: Inside a cryptomining campaign that never ran
199 malicious gems, zero working payloads: how Mend.io caught the campaign.
Never miss a post. Opt-out at any time.
You’re all set to receive our latest posts.